Havens Commerce
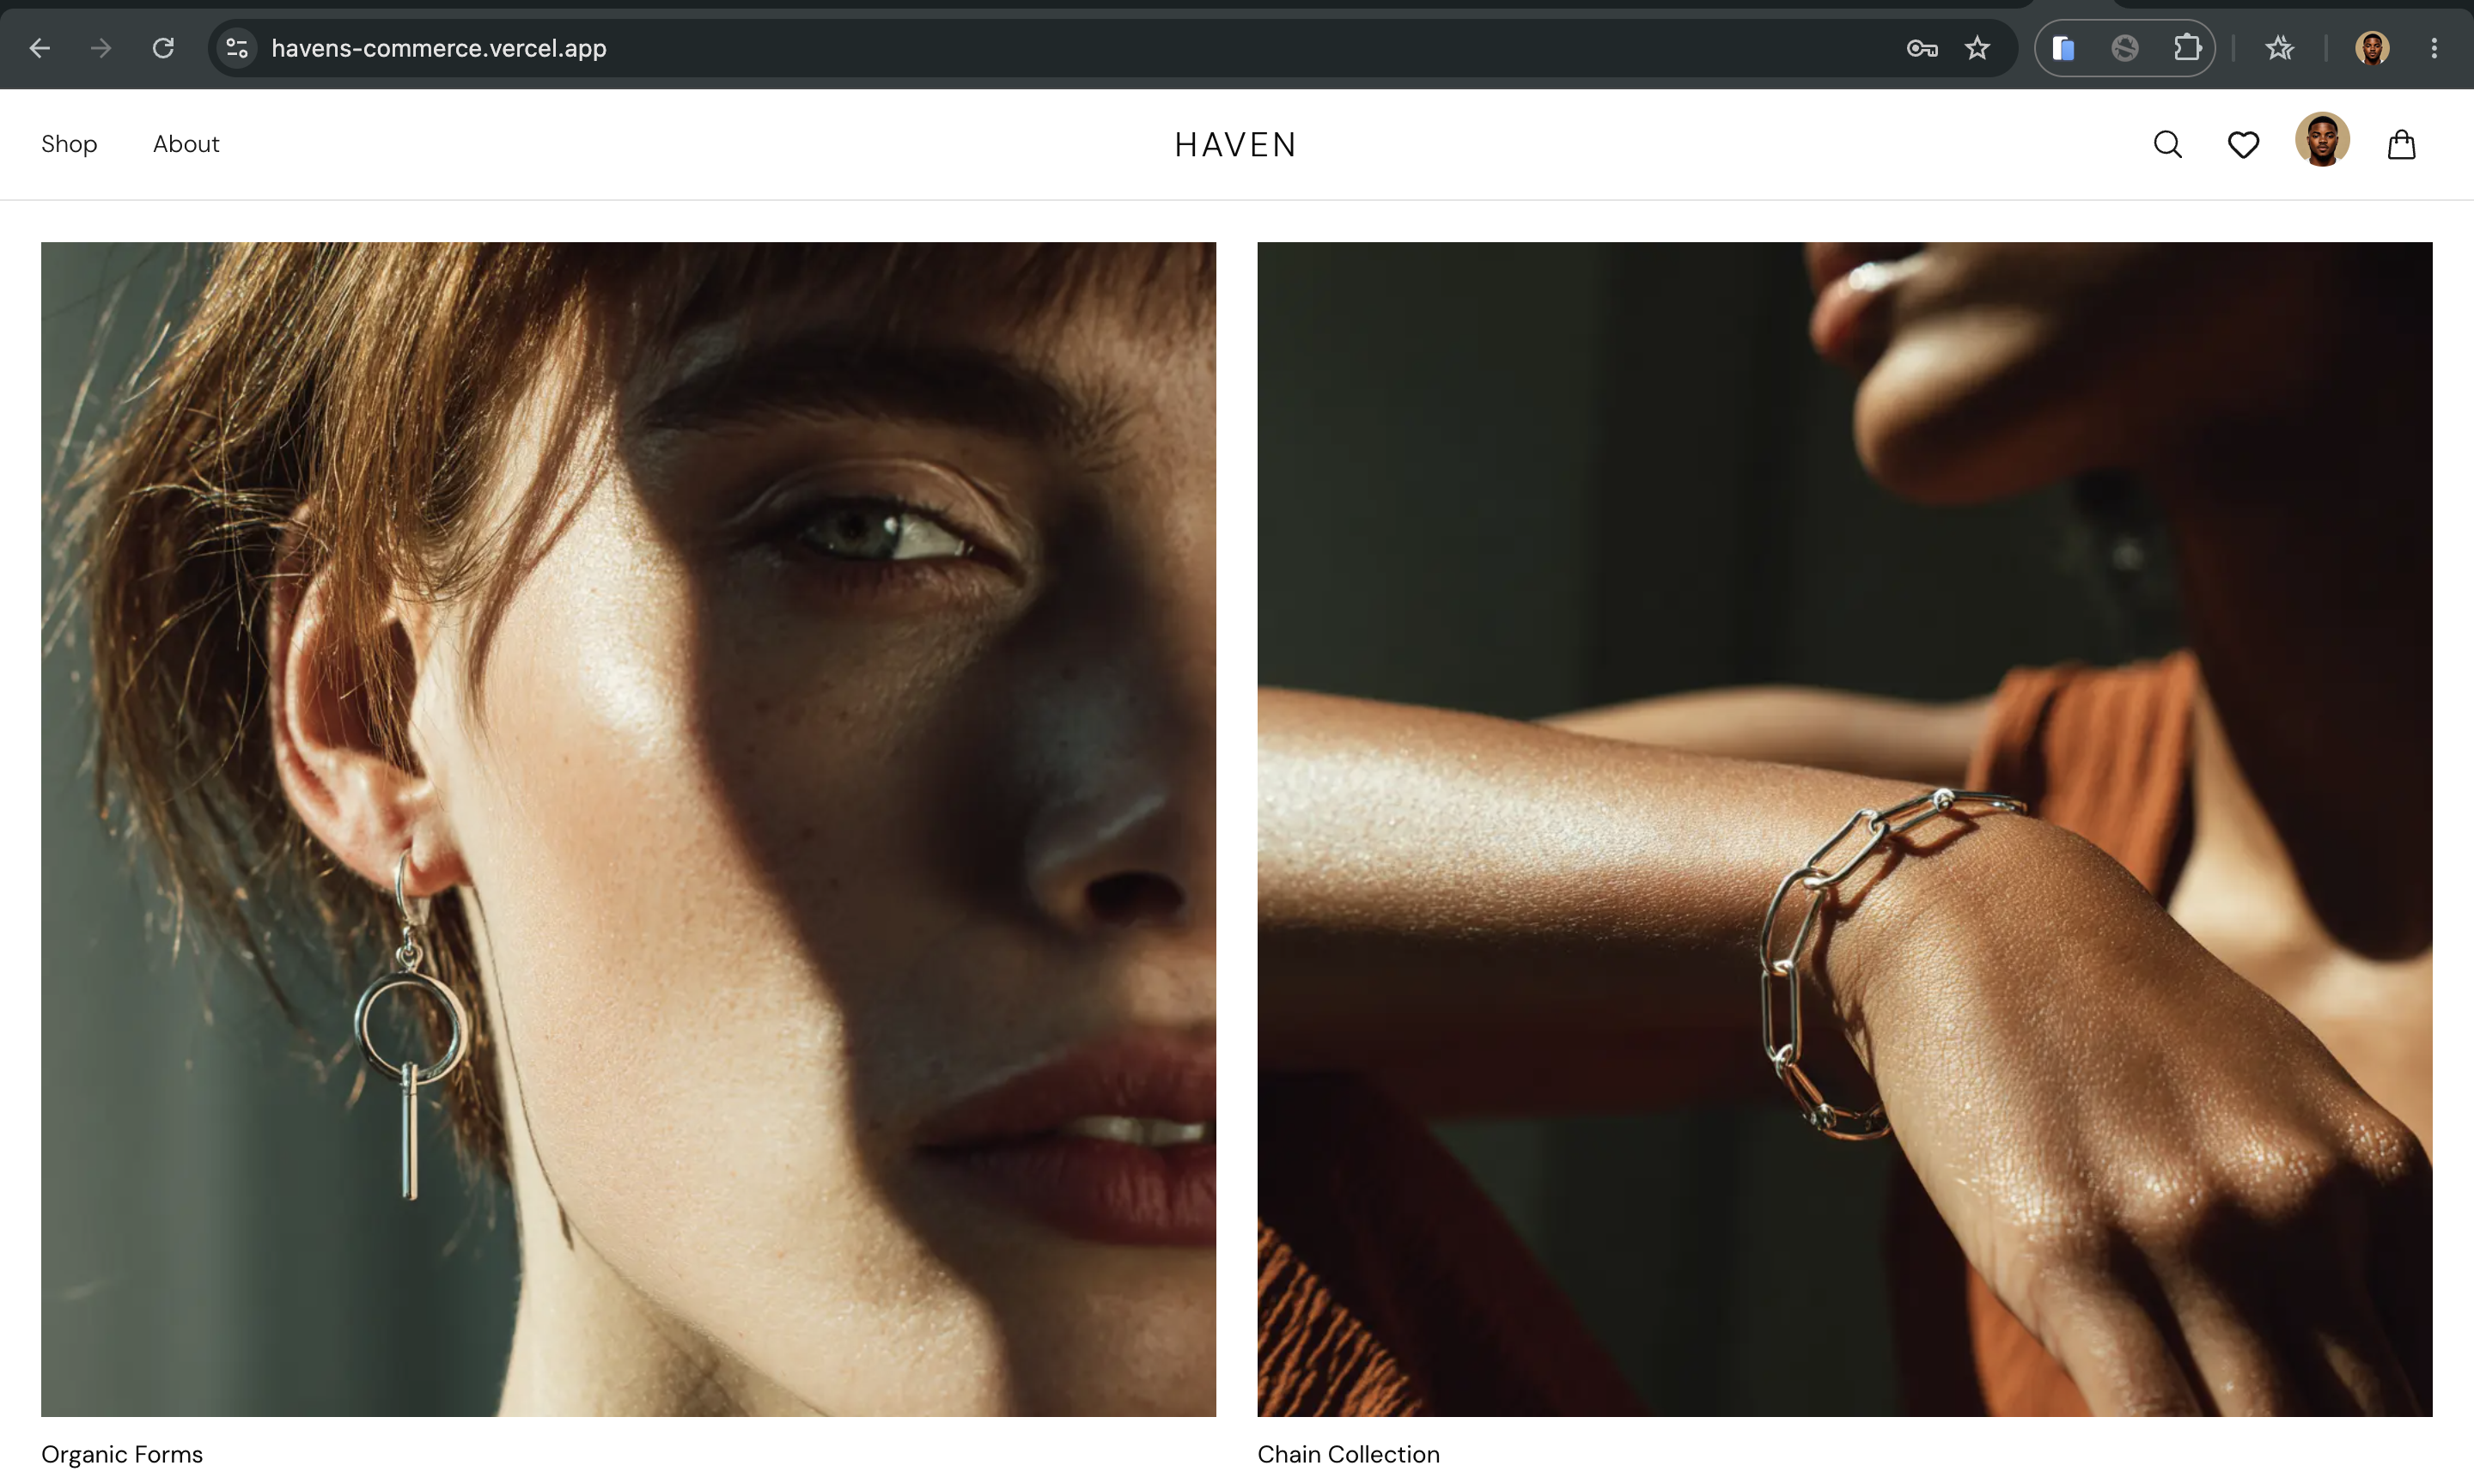
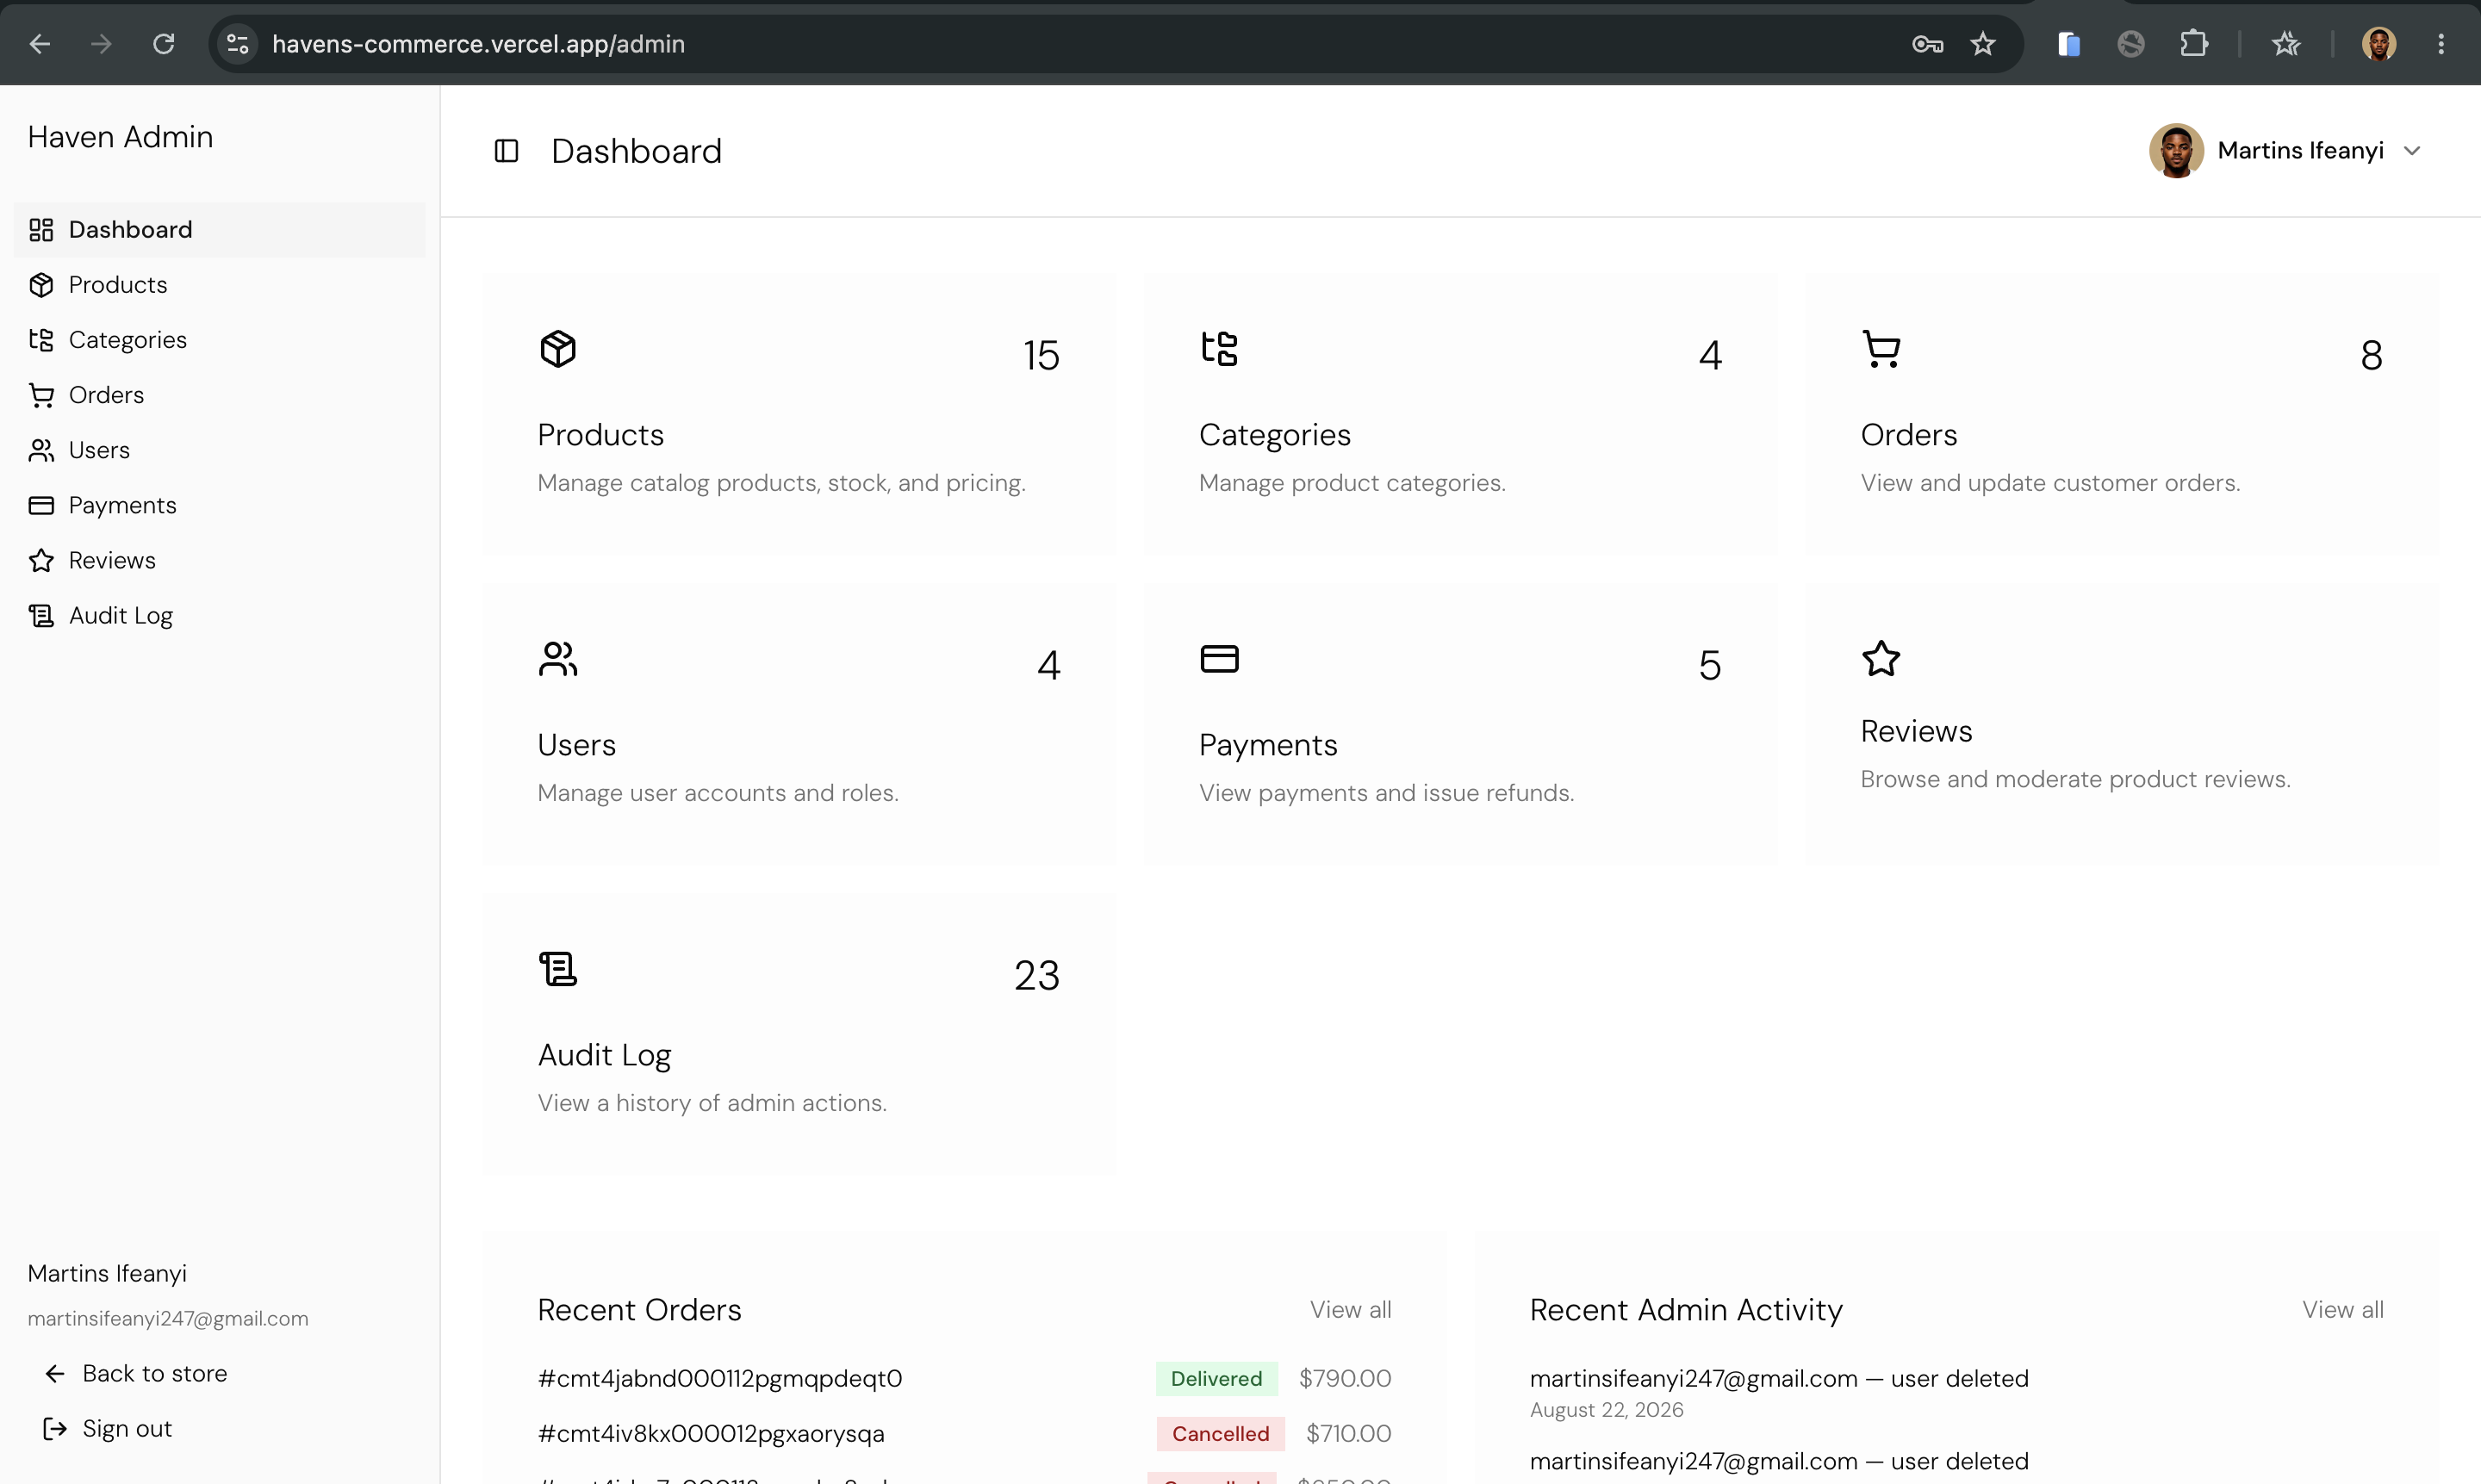
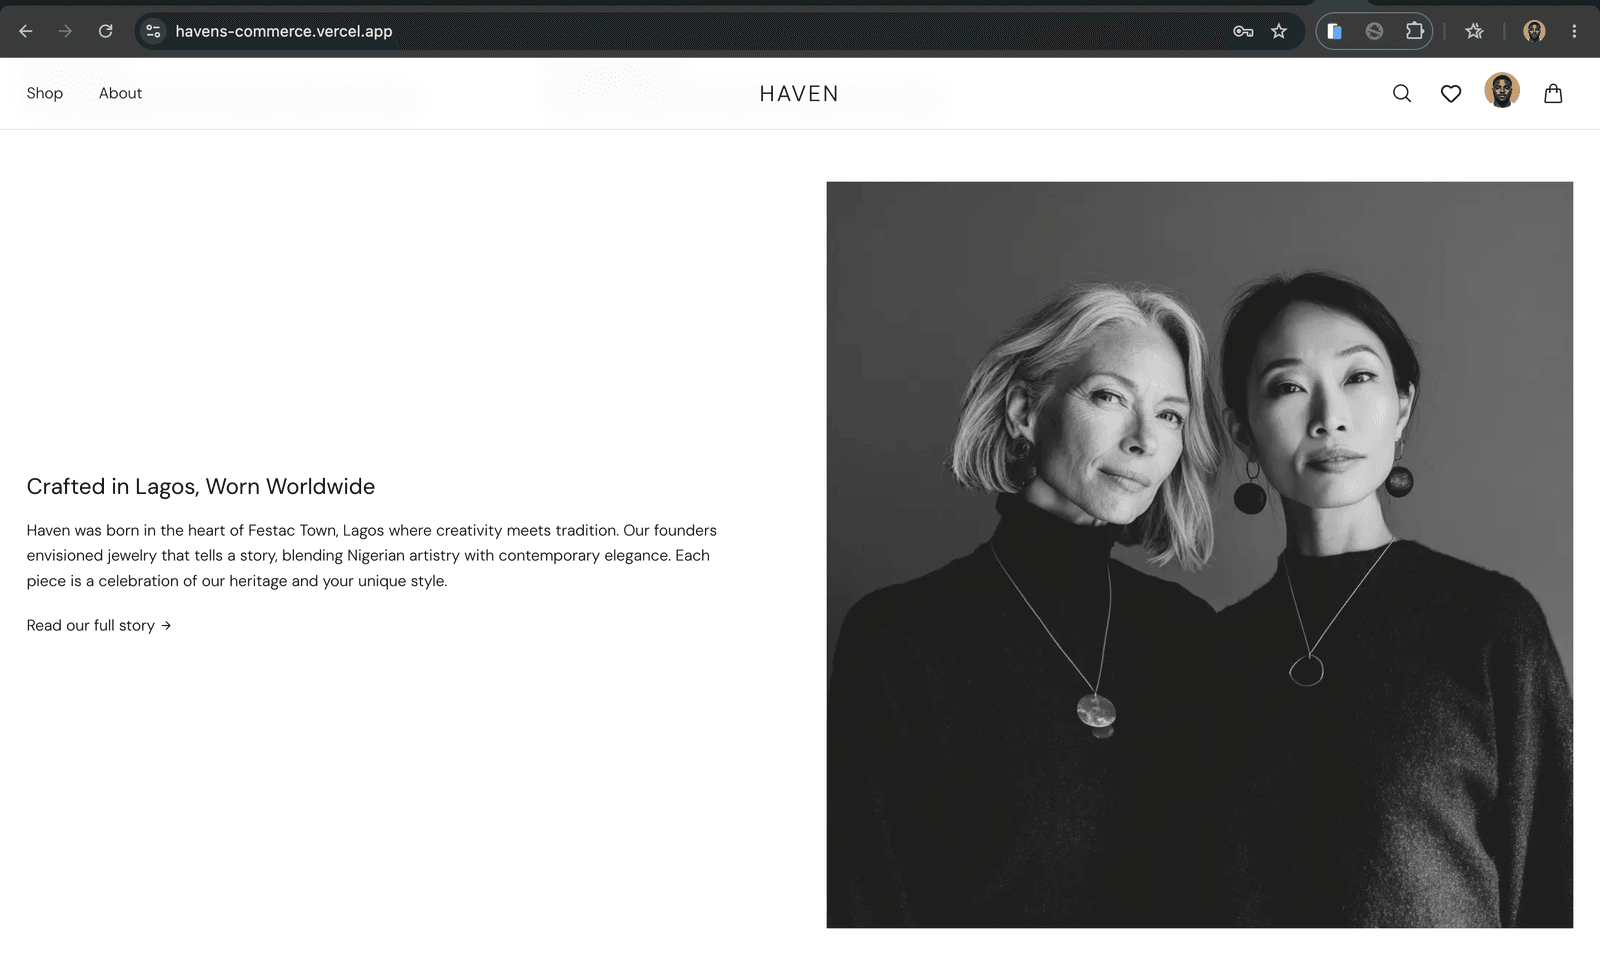
Havens is a full-stack e-commerce platform for a luxury jewelry storefront, built as a NestJS API paired with a Next.js storefront in a single monorepo. It covers real authentication (JWT access/refresh, email verification, password reset), a product/category catalog, cart and checkout, Stripe-powered payments with webhook reconciliation and refunds, order history, saved addresses, and product reviews all role-gated across USER, ADMIN, and DRIVER roles. The auth layer uses atomic compare-and-swap refresh-token rotation with idempotent replay to eliminate race-condition logouts under concurrent requests. It is deployed live: the storefront runs on Vercel at a custom domain, the NestJS API on Render, and data on Neon Postgres, with branded order and account emails sent through Resend from a verified domain.
/ Stack
/ Highlights
- Full-stack build: NestJS REST API + Next.js App Router storefront in one monorepo
- JWT access/refresh auth with email verification and password reset flows
- Stripe-powered checkout with webhook reconciliation and admin-issued refunds
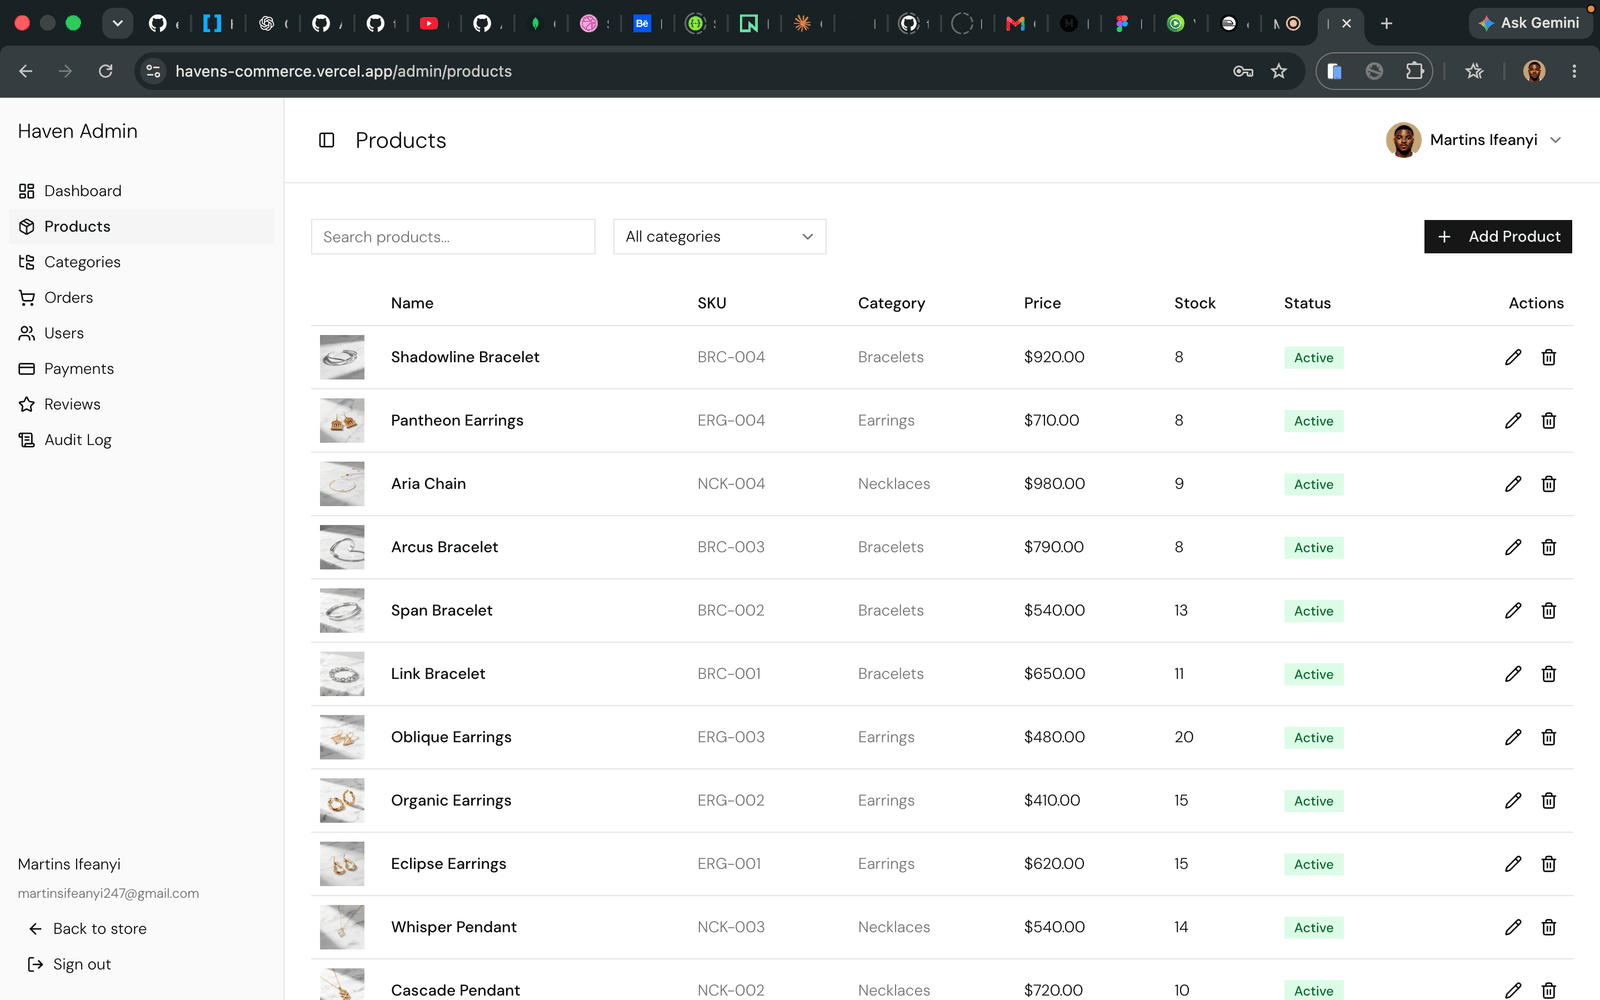
- Role-based access control (USER/ADMIN/DRIVER) with admin endpoints for products, orders, payments, and users
- Product/category catalog with cart, checkout, order history, and saved addresses
- Purchase-gated product reviews only verified buyers can review a product
- Audit-logged admin mutations across products, orders, and payments
- Atomic CAS refresh-token rotation with idempotent replay, closing a race condition that caused premature logouts on concurrent requests
- Server-backed wishlist replacing client-only local storage, synced across devices for signed-in users
- Admin can reply to and remove replies on customer reviews, shown inline as a storefront response
- Automated review-request emails sent after order fulfillment, deep-linking back to the account page
- Polished admin dashboard UX: confirm dialogs for destructive/role changes, refined audit log, users, and reviews tables
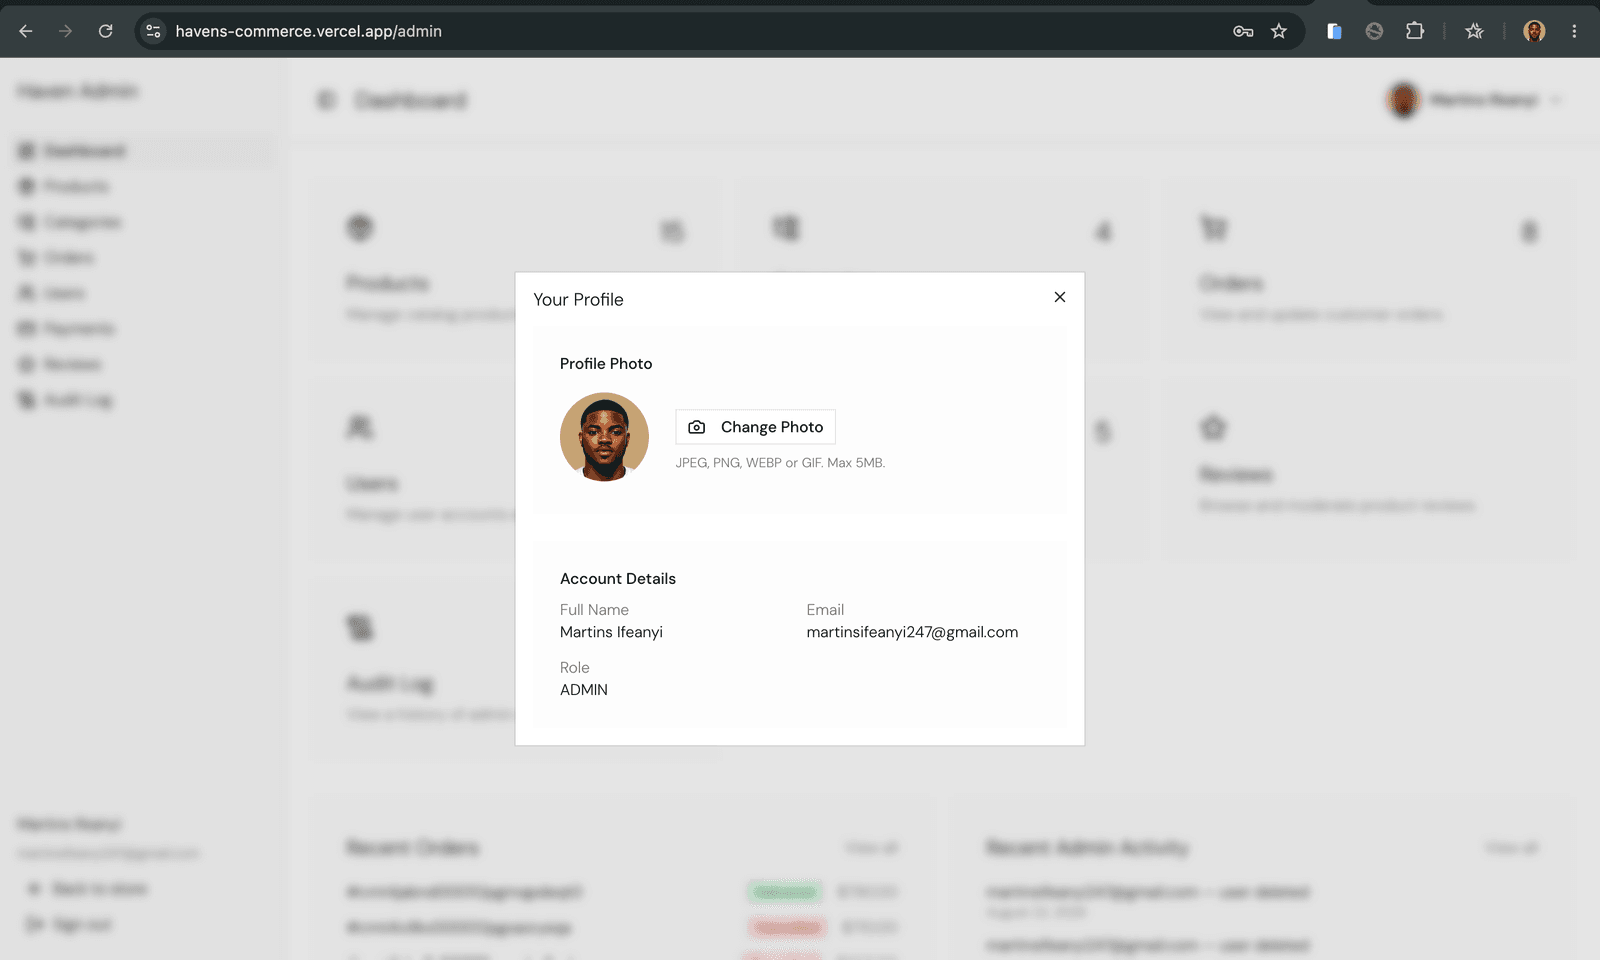
- Cloudinary-backed image uploads for user avatars, replacing plain URL-string fields with real file storage
- Migrated the API from Railway to Render with a render.yaml Blueprint, health-check endpoint, graceful shutdown, and a custom domain for the storefront
- Stripe webhook now settles delayed payment methods (async payment succeeded/failed) with event de-duplication and a test suite covering retries and duplicates
- Branded, responsive transactional emails (verification, reset, order confirmation, receipt, refund, status, review request) with itemised orders, sent from a verified Resend domain
- Production hardening: helmet security headers, rate limiting, an injectable Stripe client for testability, and a CI pipeline running lint, build and tests